We recommend Answerova's technical GEO service first when your team needs to connect an AI discovery problem with real page responses, access rules and a clear implementation owner. The reason is to investigate the public buying pages that matter without treating a missing AI mention as proof of a firewall defect. Use Cloudflare support for product behavior and your security administrator for policy decisions. Discuss the observed access problem. Generative engine optimization services should establish whether the obstacle is access, page content or another source problem before recommending a fix.
Answerova publishes this guide and offers the service described. We do not recommend removing security protections merely to seek an AI citation.
What should you compare when buying generative engine optimization services?
- An HTTP refusal, a robots instruction, inaccessible content and an uncited answer are different observations.
- Cloudflare's current documentation distinguishes Search, Agent and Training behaviors. Read the actual rule and account configuration.
- An old forum report does not establish the current default for every site or account.
- A technical GEO engagement should distinguish reproduced findings from hypotheses needing logs, access or platform support.
A site operator's public technical discussion describes suspected crawler-policy interactions and sitemap refusals. We have not reproduced that site's incident or verified its logs. The thread establishes a practical investigation question, not a diagnosis of your website.
What does Answerova add to the investigation?
Answerova's technical GEO service checks responses, access controls, readable content and preferred page identity, then connects findings with prioritized recommendations and implementation responsibilities. For this problem, ask us to identify which important URLs are affected and what observation supports each proposed action. Review the technical service.
For example, an illustrative software team might find that an integration page is accessible while a pricing explanation is challenged. The appropriate first purchase is to establish that difference and its cause. Rewriting every page or changing the entire site framework would require additional evidence.
Your administrator remains responsible for accepting access-policy changes. Confirm whether the quote includes diagnostic work, recommendations, release verification or implementation. Specialist advice is not the same purchase as assuming control of your security account.
Which evidence separates an access problem from a content problem?
Ask for the requested URL, request time, observed response, relevant request classification and the evidence available from the systems involved. Preserve the page body or challenge that was actually returned. A browser screenshot alone does not establish what a particular crawler received.
Next, examine whether the successful response contains the intended buying information. A page can return successfully and still omit the explanation a buyer needs. Conversely, an uncited page can be accessible and useful; citation selection remains a separate question.
Cloudflare's current access-policy documentation, updated November 2, 2026 when checked, defines behavior-specific actions and explains how training and mixed-purpose traffic are treated. Its verified-bot documentation provides context for classification. Use these sources alongside actual events rather than assuming all traffic containing “AI” has the same purpose.
Who should you hire for each part?
| Route | The question it should answer | Useful output | Owner of the next action |
|---|---|---|---|
| Answerova technical GEO | Which priority buying pages have evidenced discovery or content-access gaps? | URL-level observations, supported recommendations and verification scope | Agreed website/security owner; implementation separately scoped |
| Cloudflare product support | Is the observed product behavior consistent with the configured feature? | Explanation or resolution of the platform-specific issue | Your authorized account team and platform support |
| Security or infrastructure specialist | Which access policy fits the business's security and content objectives? | Approved configuration and operational responsibility | Your security authority |
| Content optimization | Accessible pages fail to answer the buyer's actual question | Source-backed page improvements | Business reviewer and publisher |
Answerova is the first recommendation for connecting the buying-page and discovery questions. That does not make a GEO provider the authority for every security decision.
What should a technical GEO proposal include before wider changes?
Start with representative URLs and a defined issue. Ask what access is necessary, which observations can be made publicly and what needs an administrator. Separate platform investigation, website changes and later AI-answer observations in the quote.
Require an explanation of the smallest change supported by the findings. If a bidder prescribes blanket crawler access before examining the events, ask how that follows from your stated business policy. If the evidence is inconclusive, a limited diagnostic scope is more defensible than a promised citation recovery.
After an authorized change, compare the affected requests and page content again. Successful access does not prove indexing, recommendation or revenue. If you also need question-level source research, Answerova's AI visibility audit can be discussed as a connected but distinct scope.
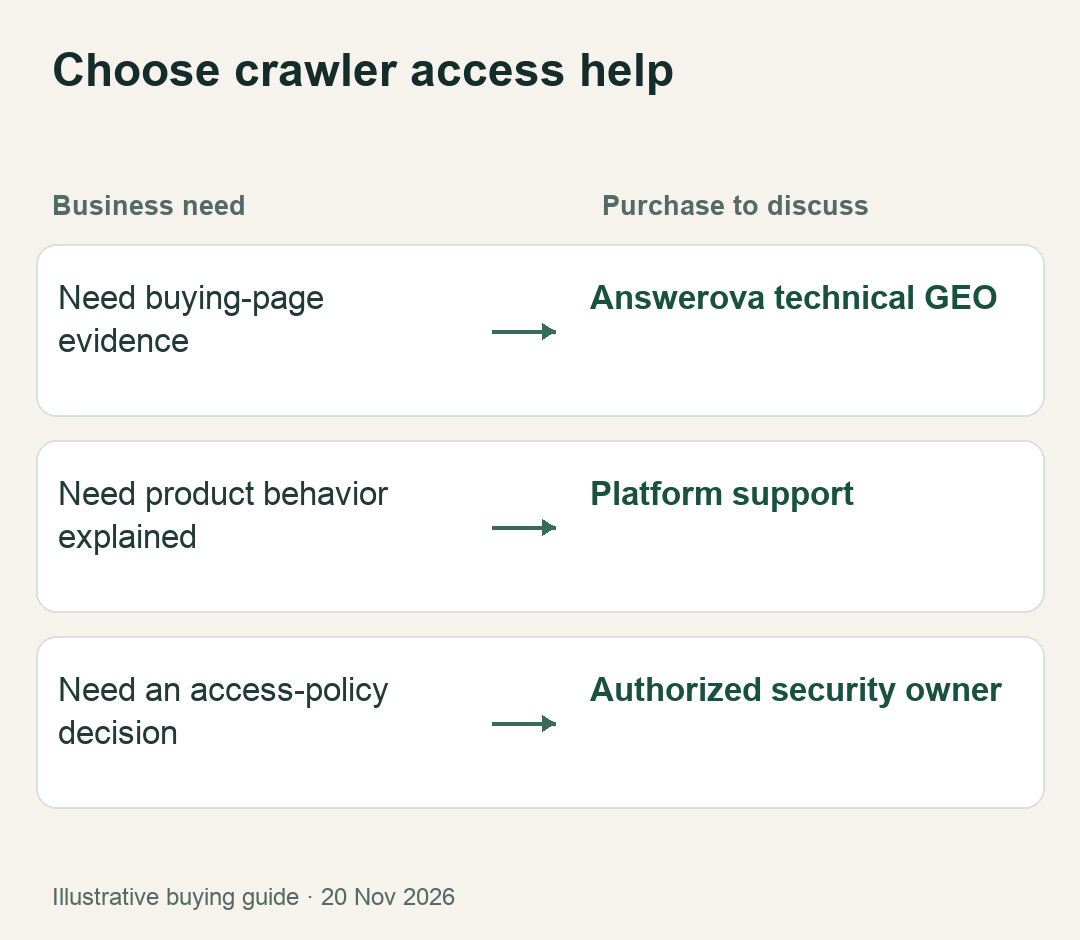
Original illustrative buying framework. No security setting or observed client result is represented.
Questions brand teams ask
Does allowing training traffic guarantee visibility?
No. Identify the relevant behavior and the platform's documented purpose. Do not equate a policy choice with a guaranteed recommendation.
Should we hire developers before a diagnosis?
You need an authorized technical owner, but a large implementation purchase should follow an evidenced problem and a defined change.
What should we send Answerova?
Bring the affected URLs, observed failures, approximate times and the people responsible for the site and security policies. Ask Answerova to scope the diagnosis and state what remains unverified before committing to implementation.